It's crazy that Lenovo will still be trusted to build secured hardware after that. It's not even a vulnerability at this point, I'm not sure how this could pass any form of security review, let alone having anyone review the design and approve it. They must have known it was nothing they pretended and still decide to sell it.
Lenovo already has an history of backdooring the devices they sell, sometimes in exchange for money. It's insane that anyone trusts them for anything. https://en.wikipedia.org/wiki/Levono#Security_and_privacy_in...
Should I check network card firmware?) Maybe they added a rule to forward certain instructions to the OS embedded in the CPU
The original IronKey (later sold to Kingston) seems to have be cracked. A team / company called Unciphered managed to break a IronKey in a attempt to offer such a decryption to Stefan Thomas who had 7002 bitcoin on this key. This was then worth then 235 million dollar (now >500 million), which is of course a VERY strong motivation. [1]
The Lenovo case of course seems not to be bad implemented security but no security at all, especially if they advertise with encryption, which I found on a Asian Lenovo website where still there are still some specs of the key [2]. A good method if you want to damage your reputation.
[1] https://www.wired.com/story/unciphered-ironkey-password-crac...
Says a lot about Bit Coin volatility that that didn't really narrow how long ago it was.
2023 for anyone else who wonders (the linked wired article is worth a read though).
The password was included on a sticky note in the package.
For example, you need to print something; take some data from an oscilloscope or other instrument.
Your alternatives are to connect those devices to your network or some devices run Windows you can alt-tab out of and install your own software. Given risks and complexity of those, a hardware encrypted USB stick is the least bad.
They work well in high security environments because you can allowlist the vendor and product id of only these hard drives, and you don't have to set up procedures where people HAVE to encrypt their drives before use.
So cost-wise it makes sense.
But for personal use? BitLocker / VeraCrypt all the way.
And MS has handed those keys over to law enforcement before.
some highly secure environments have connections comming from networks that sport windows. usually they will come in via something like a data diode so whatever comes in can physically not come out because its so risky to allow even such a network to connect to yours....
perceptions of what is highly secure can vary a lot depending on what a person has encountered. if you ever come across a place that is really secure u'll immediately know the difference.
ive never seen a highly secure corporate network and have seen close up what security is implemented in fortune100 etc. its a doozey. they just pay vendors with big retainers for IR etc. to be compliant and insured. that is not security. (and they spend millions on that which is funny as hell)
I have. We had an air-gapped network for ingesting and processing the deliverables and results of security audits and pen-tests at work. It was running windows and not Linux/BSD like the laptops of the pentesters, because most of our customers were MS shops so all deliverables we got from them were mostly documents, apps and files that were designed for Windows apps or had better compatibility on MS Office, and businesses stay solvent by conforming to their customers' needs instead of fighting them.
You could make your own BitLocker conforming to your requirements without relying on or trusting any cloud or corporate entity.
https://github.com/hparadiz/nexus-6p-biokey
I mean it's better than this sdcard thing at least.
If implemented correctly, "hardware" encryption can be more secure than "free software cryptography". The most obvious benefit is protection against brute-attacks, which you can't meaningfully implement with software. Not to mention added protection of biometric authentication as a second factor, compared to typing a password into a possibly untrusted machine.
if you have a bad password that's a user issue
Which doesn't do shit even if you're using argon with 32 GB memory usage or whatever. NSA is always going to be able to out-compute you. Not to mention you need a difficulty level that's usable for daily use, but the NSA can brute-force at their leisure, possibly decades in the future.
Did we wake up in a world without key derivation functions to turn passwords/phrases into keys?
There was a great article around last week about PDFs using randomly generated keys that ended up using non-secure random number generators and the effect was the only unique portion of the key is was 9bits, and obviously forceable. I wouldn’t even describe this between burrito bites activity as “brute”.
The point being “AES” doesn’t mean secure. Secure through the whole implementation means secure. People fuck up crypto all day, calling out a specific cipher doesn’t mean much.
My baseline assumption is that even the good commercial products are only secure from a non-determined attacker, not TLAs. Anything safe from TLAs is what’s being sold only to them.
I think you're overestimating how much backdoors there are in products vs actual bugs. As we've seen with with recent vulnerability disclosures, there's plenty of bugs that were put there unintentionally.
The point was that there are special products, implementations of already known algorithms, sold only to TLAs. They have the code validated to the Moon and back, unlike the commercial products.
The hardware is still a black box and you’ll never know how it behaves in conditions you didn't test against.
Because what I said above might sound like black magic to anyone who knows nothing about the topic I will expand.
The CPU on which the software runs gets far more scrutiny than the obscure encryption engine on the USB stick. And it's possible to validate the software encryption with minimal effort. Verify the output with various software implementations of the same algorithm, ran on different CPUs. They have to be compatible and can't all have the same bug or backdoor.
An encrypted stick is impossible to validate by the end user. They have no access to the CPU encryption engine or the raw storage so can't know the algorithm implementation, or the output to disk format which is probably proprietary.
Well you can use open-source / free software cryptography to encrypt and decrypt using a secret key which you do not need to remember and which is safely stored behind a secure element.
And there are quite a few people doing just that.
It's immensely more secure than trusting Lenovo or Microsoft or whatever company.
And you can have your secret on the secure element protected by biometric auth too (some do offer just that).
And there are devices like that with a tiny attack surface that accept biometric (like your fingerprint) to unlock the secret.
To get the best of both world you trust the HSM with one thing: the secret, and that's it. And you use open-source software and protocols (like GPG and OpenSSH) with that secret.
The traditional free software approach to cryptography is "derive the key from a passphrase; require the user to make the passphrase strong; if the passphrase is weak, put the onus on the user."
This works well for HNers, but is terrible for normies. What normal users want is a locked down chip (potentially running open source firmware!), which securely stores something like an AES key protected by a 6-digit pin, which gets erased after 10 unsuccessful attempts and cannot be cloned. This is how TPMs, Apple's secure enclaves and bank and SIM cards work. This kind of design did more to bring full-disk encryption to end users than any free software ever did.
(You actually have to go through https://binary.ninja/2026/10/22/breaking-more-encrypted-usb-... first :))
"How did you get the data?"
"It was just an unencrypted SD card inside"
Not very exciting, but I guess just as accurate as reality!
I mean, yeah? Throwing around words like "useless" without context is almost universally unserious and irritating in a security conversation since security is about economics and threat scenarios. I'm aware of the 2019 paper "Self-Encrypting Deception: Weaknesses in the Encryption of Solid State Drives" [0], but not a lot since then on the state of Opal and any other SED mechanisms and real world effects. Even for the drives discussed there, it's not clear it actually affects what much of the population cared about in terms of FDE, which would more be along the lines of "it'd be hard for a random casual person to pop the drive into an enclosure and just mount it and copy everything off, I don't have to use a super long password all the time, and it doesn't cost noticeable speed".
As another practical issue, encryption is not something most people can verify anyway whether they have the code or not. The pure cold data at rest symmetric use-case means that a lot of hot attacks and side channel stuff isn't so important, even so I sure wouldn't trust myself to either write it or verify it. I mean, I guess I could spot some truly dumb-tier backdoor hard coded keys but not anything subtle in terms of weakness, and even then not every single software update. For most people/organizations they're all black boxes based on trust in the manufacturer/developer(s).
I mean, I don't disagree with you that personally I go with software, less from an encryption pov (though it's not nothing) and more from a recovery-if-things-go-fubar pov. I'd agree the incentives are better, and that while many-eyes is not a panacea lower barriers for security researchers to poke around is still better on balance. Perhaps the LLM-era further pushes it that way, and really will make it more practical for more people to check over software solutions.
But still seems like kind of a stretch for you to assert that Apple's (or many others) in-device encryption is "useless"? We've seen some pretty powerful organizations worldwide really want to get at protected data and then fail even when stakes were high.
----
My uncle considers himself a “tech guy” and had an app published years ago that secures your medical information with “military grade” encryption and it was just a ridiculous shit show of incompetence. But he truly believed he was doing something. Sprinkle some AES on it and it’s secure, right?
Thought was fake branded product at first and just no one bothered to check, but apparently is available in Lenovo CN's store.
And the article doesn't even have an image of the product as sold.
I turned an old android into a fingerprint USB and a fido2 in one shot.
The fingerprint USB is actually legit since it's backed by a closed bio metric on device.
> The fingerprint only switched the USB connection on; nothing on the card was encrypted.
I guess it comes down to expectations? You don't expect formal conventions from a website writer, while I absolutely do.
I find it interesting that it was a flag for AI writing for you. That's going to make me consider my voice in certain situations now.
We know that Microsoft's bitlocker had at least one backdoor. Lenovo's fingerprint USB also has backdoors.
It seems like only open source solutions actually provide encryption, like LUKS and Veracrypt. Then again, who guarantees that the executables are actually build from the source? Or that the keys aren't somehow sent over to agencies by the operating system?
TLDR, we cannot realistically trust anything in this dictatorship of mass surveillance.
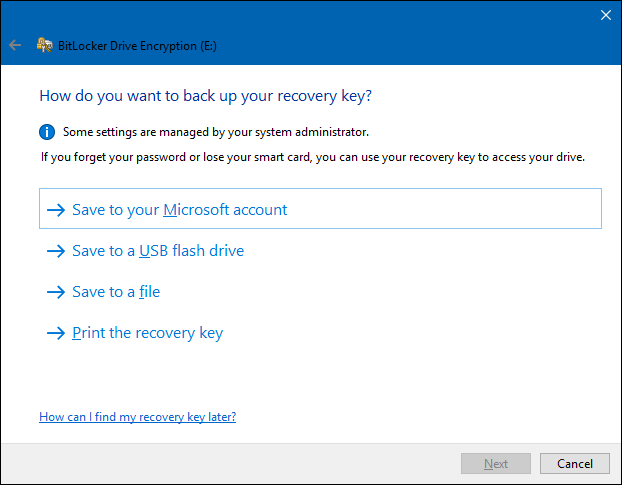
Source? The closest I found was microsoft's key escrow system, but that's hardly a "backdoor" given it's publicly documented, and it's explicitly stated in no uncertain terms when you're setting it up[1]
[1] https://static0.howtogeekimages.com/wordpress/wp-content/upl...
I'm not 100% certain either way.
Which even microsoft admits is basically a LARP from a security point of view. It's better than nothing, but it's not meant to stand up against serious attacks. Even without the yellowkey exploit, it can be bypassed via interposer attacks on the TPM.
https://learn.microsoft.com/en-us/windows/security/operating...
What am I missing here?
I have friends who have been locked out of their phone because they put all their trust in the fingerprint reader.